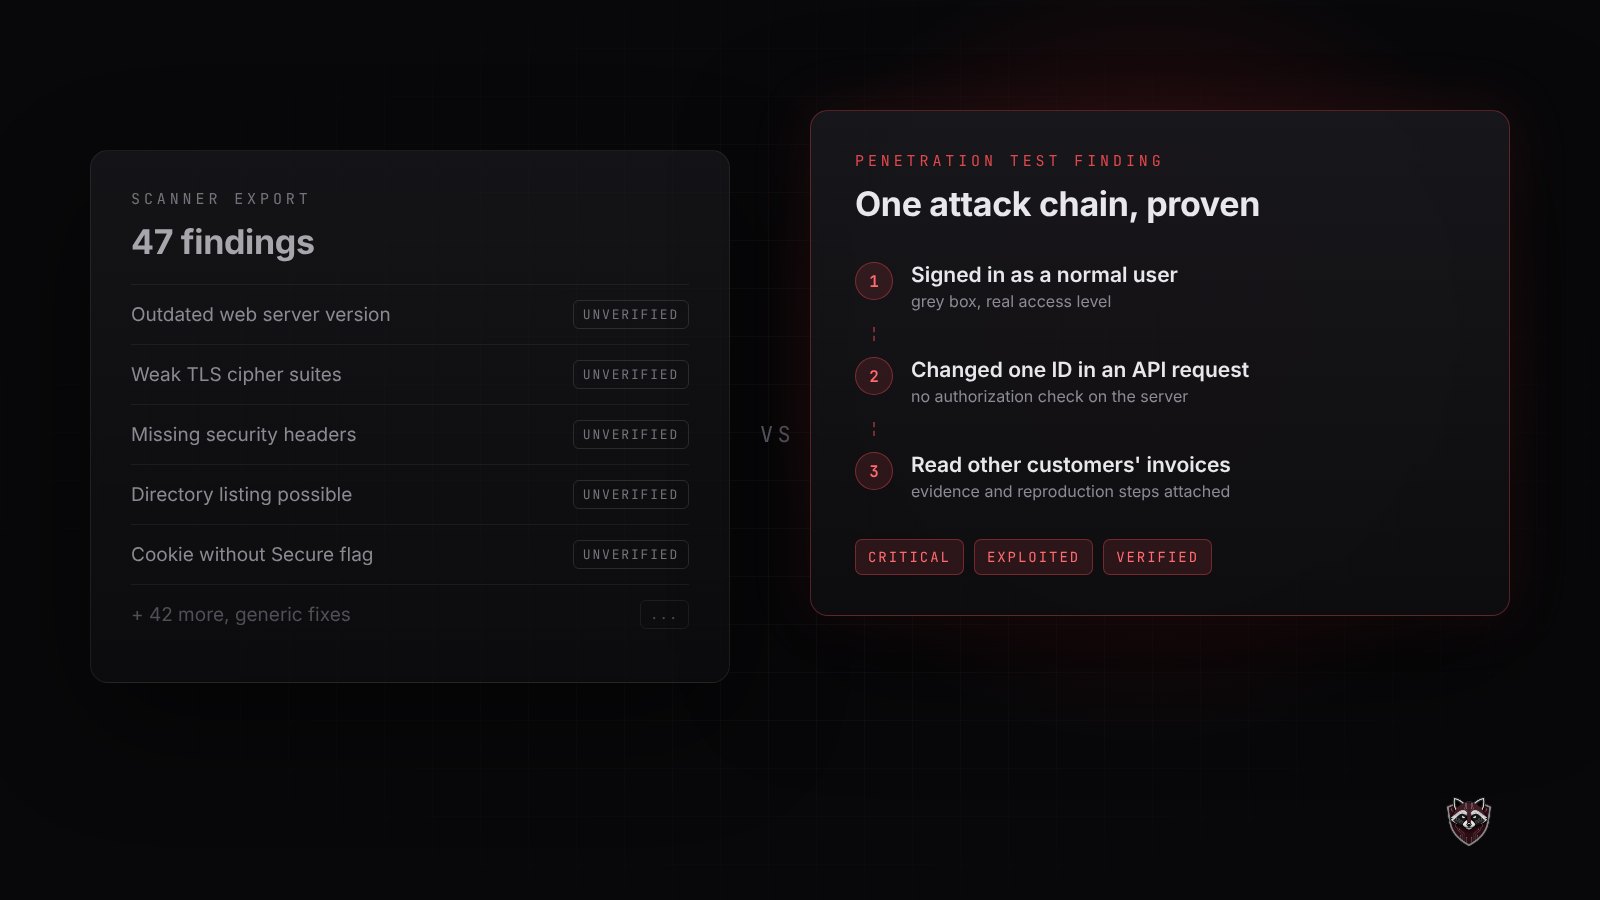
Vulnerability Scan vs Penetration Test: Another Day, Another Fake Pentest
/ 10 min read
A scanner report with a pentest cover is not a penetration test. See the real difference, how to spot a fake report, and where AI actually helps testers.
Notes from the engagements: how attacks actually work, what we keep finding, and what to do about it.
Most security writing is either a vendor pitch with a diagram on it or a research paper aimed at other researchers. This is neither. These are the things we end up explaining on calls often enough that they are worth writing down once.
Expect plain language and specifics: what an attack chain actually looks like end to end, why a class of bug keeps surviving code review, what a finding costs you in practice, and what to do first when you have twenty of them and time for three.
Everything here comes out of real engagements. Nothing is written up in a way that identifies a client, and nothing goes out that has not been fixed.
/ 10 min read
A scanner report with a pentest cover is not a penetration test. See the real difference, how to spot a fake report, and where AI actually helps testers.
/ 4 min read
What a penetration test costs, what drives the price up or down, why cheap tests are often scans in disguise, and how to cut cost without weakening it.
/ 4 min read
How long a penetration test takes, what actually gets tested, how black, grey and white box testing differ, and the one thing we need to start.